
 Search within the site
Information Security
Basic Concept
Recognizing the Importance of Information Security
The use of information and IT is essential to corporate activities, and Konica Minolta understands that ensuring information security is of paramount importance in effectively utilizing the various types of information it holds. Konica Minolta believes that managing information appropriately in light of risks such as information loss, leakage, and destruction contributes to business continuity and enhances customer trust, and is therefore committed to continuous improvement in this area.
Konica Minolta Information Security Policy
Guided by our management philosophy of “The Creation of New Value,” we at the Konica Minolta Group are committed to providing products and services that contribute to the development of society.
We are dedicated to maintaining information security (confidentiality, integrity, and availability), which is one of the most important issues related to business activities. Given this commitment, our basic approach to information security is to continuously make improvements by measuring and assessing risks associated with important information assets, and applying effective measures to mitigate those risks.
“Management Based On Facts”
1. Direction of Information Security Initiatives
We will strive to continually provide products and services and develop sound businesses while recognizing our obligation to protect information assets handled in the course of business activities.
2. Compliance with Laws and Other Requirements
We will comply with the legal requirements of Japan and other countries related to information security as well as social norms, internal company standards and contractual security obligations. On this basis we will properly accommodate agreements made by the international community.
3. Establishment of Information Security Management System
We will establish an information security management system in order to appropriately grasp business risks and changes in the risk environment and to establish and maintain response strategies. We will work to maintain, further develop and revise the system by establishing objectives for information security.
4. Risk Response
As a manufacturer we will deal with a broad range of risks related to activities from development and production to sales and service. For risk assessment, we will establish criteria to assess the relative importance of each information asset and stringently manage our assets based on these assessments.
5. Protection from Threats
We will take appropriate measures in order to protect information assets from threats such as accidents, hindrances or improper activity that would prevent the assets from being properly utilized, and in order to prevent information assets from being lost, damaged, altered or divulged.
6. Information Security Education and Training
We will provide the necessary education and training to all employees and will carry out business while recognizing our societal responsibility to use and manage information assets appropriately.
7. Continuous Improvement
We will strive to continuously make improvements by reviewing this information security policy and our management measures on a regular basis, and as necessary, within the framework of our information security management system.
8. Active Disclosure
We will communicate risks to stakeholders and be accountable to them. This policy will be disclosed to all employees and outside parties.
April 1, 2022
Toshimitsu Taiko
President and CEO
Konica Minolta, Inc.
Structure
Konica Minolta has established the Security Management Board (SMB), comprising the officers in charge of information security, and the Security Management Office (SMO), which serves as the organization responsible for promoting information security initiatives, as part of its Group-wide information security governance structure. Using this framework, Konica Minolta is continuously working to improve information security levels worldwide.
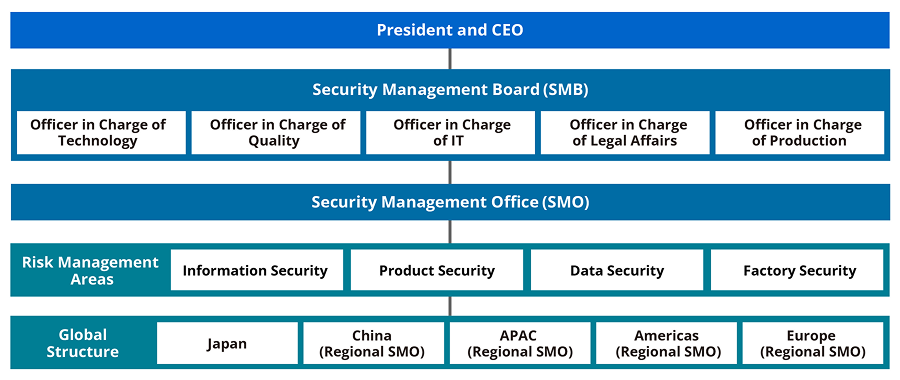
In the Konica Minolta Group in Japan, an information security management system implementation structure has also been established under the leadership of the President and CEO and the officer in charge of the IT planning and management organization, who has been appointed as the person responsible for overall IT security. .
Initiatives
Information Security
In order to ensure the security (confidentiality, integrity, and availability) of information under management, including not only information managed through IT systems but also information in paper-based media and information relating to services and personnel, all Group companies in Japan have continuously maintained ISO/IEC 27001 certification, the international standard for information security management, since 2009. As part of these activities, information security risk assessments are conducted once a year, and risk response plans are formulated and implemented for high-risk items. Meetings of information security promotion managers, attended by representatives of each business, are also held quarterly. At these meetings, activities — primarily the progress of risk response plans and summaries of incidents — are reported to the person responsible for overall information security management, who instructs the needed responses, thereby driving the PDCA cycle.
Furthermore, measures to prevent unauthorized use and information leakage are implemented through the establishment and operation of rules for managing confidential information and systems for restricting and monitoring access to and removal of confidential information. Education on personal information protection and information security is also provided at least once a year to all employees of Group companies in Japan, from officers to non-regular employees.
Outside Japan, Group companies are also encouraged to obtain ISO/IEC 27001 certification. In addition, all Group companies outside Japan are required to provide IT security education to all employees at least once a year.
In response to today’s increasingly serious cyberattacks, Konica Minolta implements global IT security measures based on the Cybersecurity Management Guidelines formulated by Japan's Ministry of Economy, Trade and Industry. With management recognizing the importance of addressing cyber risks, Konica Minolta has established a Group-wide incident response structure (KM-CSIRT*) and reporting and response processes for incident and vulnerability information.
In addition, to ensure the continuity of IT services necessary for business continuity at Konica Minolta, IT Service Continuity Management (IT BCM) has been introduced in each organization. Guidelines for developing IT Service Continuity Plans (IT BCP) have been established, and IT BCP assessments are conducted once a year.
Konica Minolta also promotes IT security controls, which form part of the IT controls required under the Financial Instruments and Exchange Act (J-SOX), while ensuring consistency across the Group.
*KM-CSIRT (Computer Security Incident Response Team): Konica Minolta’s security incident response team.
| FY2023 | FY2024 | FY2025 | |
|---|---|---|---|
| Number of information security incidents | 7 | 5 | 9 |
* The figures represent the number of incidents determined to be reportable to KM-CSIRT based on Group-wide reporting criteria, regardless of whether any actual damage occurred. The number of reported incidents may also vary depending on the extent to which incident detection and reporting processes have been established throughout the Group.
All reported incidents are addressed under the leadership of KM-CSIRT through an established response process, including initial response activities (identifying the scope of impact and containing the incident), investigation of the cause, recovery, and the development and implementation of measures to prevent recurrence. Furthermore, in coordination with relevant internal departments, a framework is in place for notifying customers, business partners, and other related parties and reporting to regulatory authorities in accordance with applicable laws, guidelines, contractual obligations, and other requirements. In the fiscal years shown above, there were no incidents determined under the Group's criteria to have a significant impact on business operations or incidents requiring public disclosure under applicable laws and regulations.
Factory Security
Konica Minolta is working to strengthen factory security across the Group. By taking steps such as establishing guidelines that take into account the specific characteristics of each factory, isolating factory networks from IT networks, and strengthening business continuity planning (BCP), Konica Minolta is working to reduce the risk of production stoppages.
Product Security
Konica Minolta is working to strengthen product security across the Group. For details of these initiatives, please refer to the link below.
Protection of Personal Data
Basic Approach to the Protection of Personal Data
Konica Minolta respects the interests and privacy of individuals and is committed to the appropriate handling and protection of the personal data of customers, business partners, officers, and employees.
Personal Data Protection Structure
Under the leadership of the person responsible for overall personal data protection, who is appointed by the President and CEO, Konica Minolta has established a basic framework within the Group and promotes the protection of personal data to ensure that personal data processed by the Group is managed appropriately and in compliance with applicable laws.
Personal Data Protection Initiatives
Konica Minolta has established the Global Personal Data Protection Policy and Regulation for Protection of the Personal Data of Konica Minolta Group in line with Japan’s Act on the Protection of Personal Information and the EU General Data Protection Regulation (GDPR), among other laws and regulations, and appropriately obtains and manages personal data in accordance with applicable laws and regulations in each region.
Konica Minolta also uses various training programs and e-learning to ensure awareness of the policy and regulations, as well as compliance requirements in each region.
Furthermore, if a leak of information held by Konica Minolta, including personal data, is confirmed or suspected, the matter is reported to the officer responsible for overall personal data protection under the KM-CSIRT framework. The facts and extent of the impact are then immediately assessed, and a system is in place for reporting the incident to personal information protection authorities in each country, such as the Personal Information Protection Commission in Japan.